AI Products
AI LabsOpenAI AgentsClaude AgentsGrok BotWorkstation CRM (WSL CRM)MarketingAll Products
AI Solutions
Applied AIAI AgentsGenerative AIAI AutomationAI UpskillingAI SME PackagesEnterprise AI LabAI WorkstationsPrivate AIGPU ClustersEdge AIAI by Industry
AI Services
Platform ModernisationDigital EngineeringData Foundations & AIAutonomous OperationsAI ConsultancyDevOps AutomationCyber SecuritySoftware DevelopmentAgent BuildingMLOps Setup
About Us
PartnersCustomer Stories
AI InsightsJev seriesBenchmark LabModel selection
Articles
Documentation
ToolsWSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7
News
Blog
Contact UsLogin

AI workstations, AI Multi Agentic Software, GPU infrastructure, and intelligent agent solutions for modern businesses.

Contact Us

AI Solutions

Applied AIAI AgentsGenerative AIAI AutomationAI UpskillingAI SME PackagesEnterprise AI LabAI by Industry

Products

All ProductsWSL CRM & ERPMarketingOpenAI AgentsWSL ProxyRing PromoterWSL VaultJobshoutSysOps 24/7

Company

About UsWhy WorkstationPartnersCustomer StoriesPricingContact

Resources

AI InsightsArticlesDocumentationBlogSearchSitemap
UK Office
77-79 Marlowes, Hemel Hempstead HP1 1LFDirections - Take Junction 20 off M25 Outer LondonCompany No: 11641870Mon - Fri: 9:00 AM - 6:00 PM GMT
+44 7515 356 146
Belgium Office
Workstation SRL, Rue Vanderkindere 34, 1180 Uccle, BrusselsBE 0751.518.683Mon - Fri: 9:00 AM - 6:00 PM CET
+32 492 45 67 46
India Office
#159 Sector 9, Pocket 1, DDA Flats, 110077 Dwarka, New Delhi
+91 98881 98841

© 2026 Workstation AI. All rights reserved.

PrivacyCookiesTerms of ServiceWebsite Sitemap

Loading blog...

Home / Blogs
DevOpsSecuritySREKubernetesAI

WSLVault: Steal the Server. Not the Secrets.

Open-source secrets manager with envelope encryption, true multi-tenancy, KV/transit/PKI/leases, multi-region HA, and hash-chained audit

Balinder WaliaSeptember 22, 20261 min read

Steal the server. Not the secrets. WSLVault is an open-source, self-hosted secrets manager built on AES-256-GCM envelope encryption and a per-tenant key hierarchy. This intro covers what it is, why the model matters, and how you drive it from console, CLI, or SDKs. Deep dive: long article · Product: /wsl-vault.
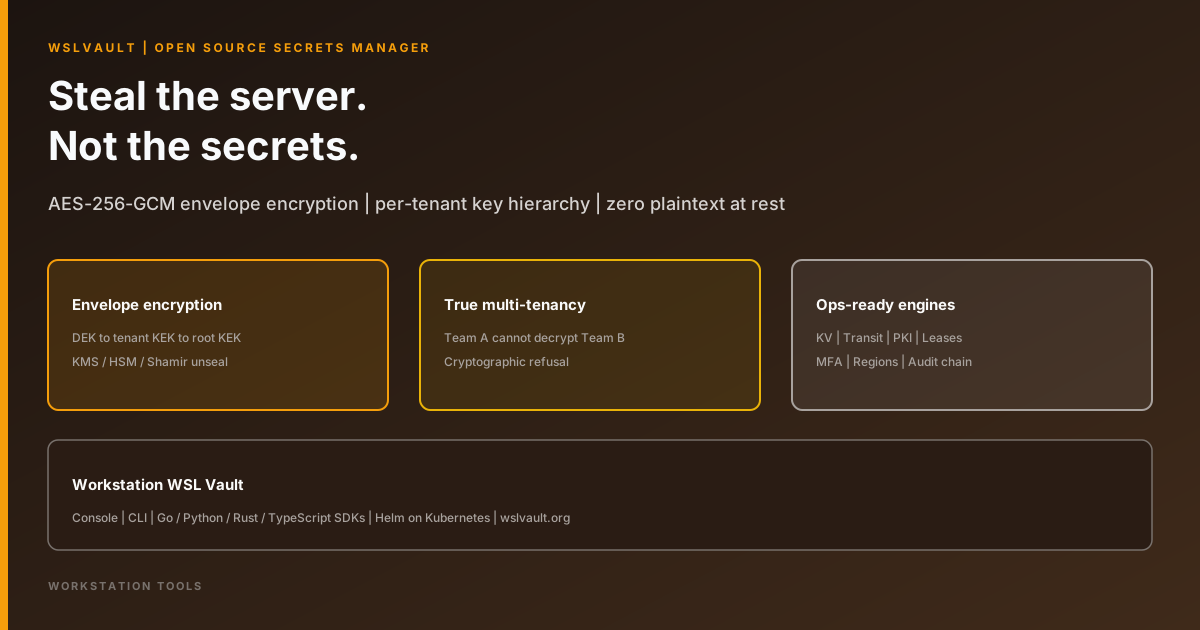
WSLVault — steal the server, not the secrets

Watch on YouTube (~20 min)

Bottom line. A stolen disk, database dump, or compromised host should leave attackers with ciphertext they cannot open. WSLVault seals every secret before storage — DEK → tenant KEK → root KEK — so multi-tenancy is cryptographic, not cosmetic.

WSLVault is built for operators who want Vault-compatible workflows without plaintext at rest: Rust services, Helm/GitOps on Kubernetes, CLI plus Go/Python/Rust/TypeScript SDKs, and a steel/brass web console.

What you will learn

  • True multi-tenancy — Team A cannot decrypt Team B (cryptographic refusal, not “oops”)
  • Envelope encryption — DEK → tenant KEK → root KEK (KMS / HSM / Shamir)
  • Engines — KV secrets, transit encryption, PKI, dynamic leases, MFA
  • Operations — Active/active multi-region replication and tamper-evident, hash-chained audit
  • Why it matters — Steal the disk ≠ steal the secrets
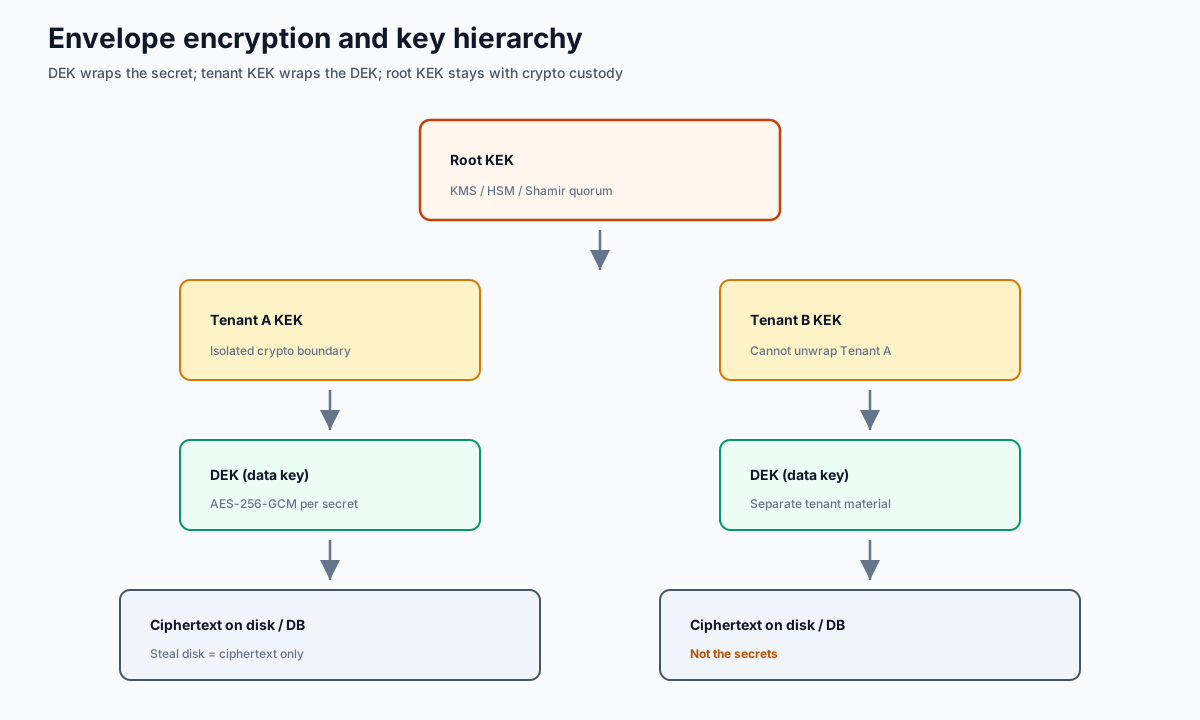
WSLVault envelope encryption key hierarchy

Links

  • Site: https://www.wslvault.org/
  • GitHub: https://github.com/bwalia/wslvault
  • Docs: docs/
  • Getting started: GETTING-STARTED.md
  • Workstation product page: /en/wsl-vault

Read the full technical brief · Open the WSL Vault tools page